Friday · 2026

Security roundup

6 stories · 5 outlets · 4 min read

Tokenization flaws and AI-code risks dominate

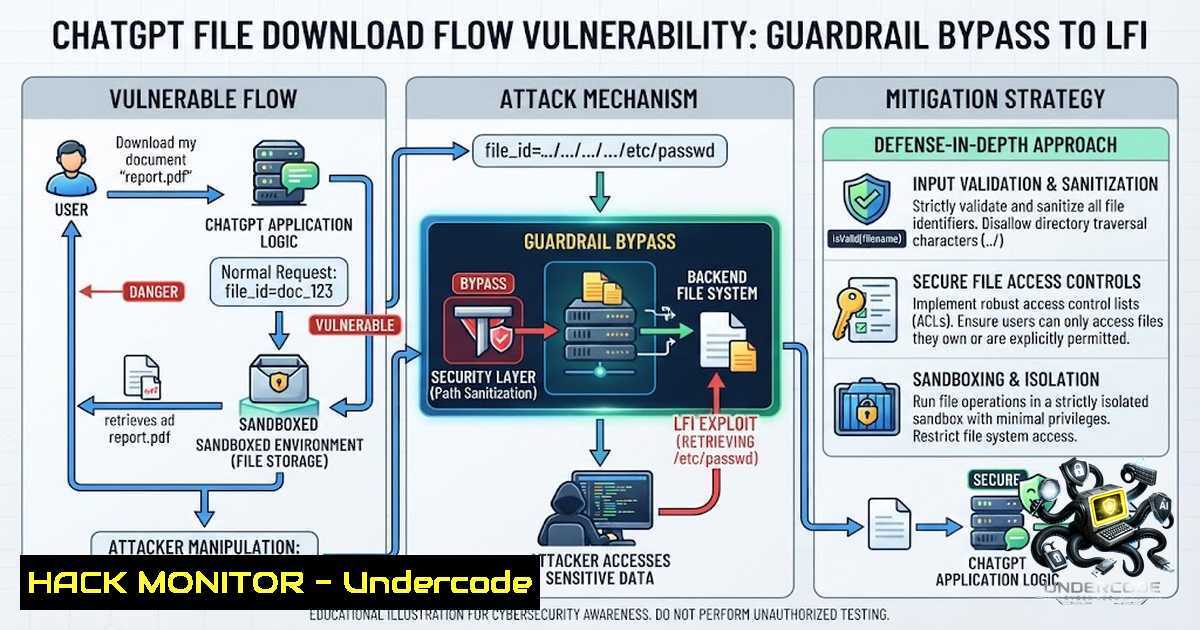
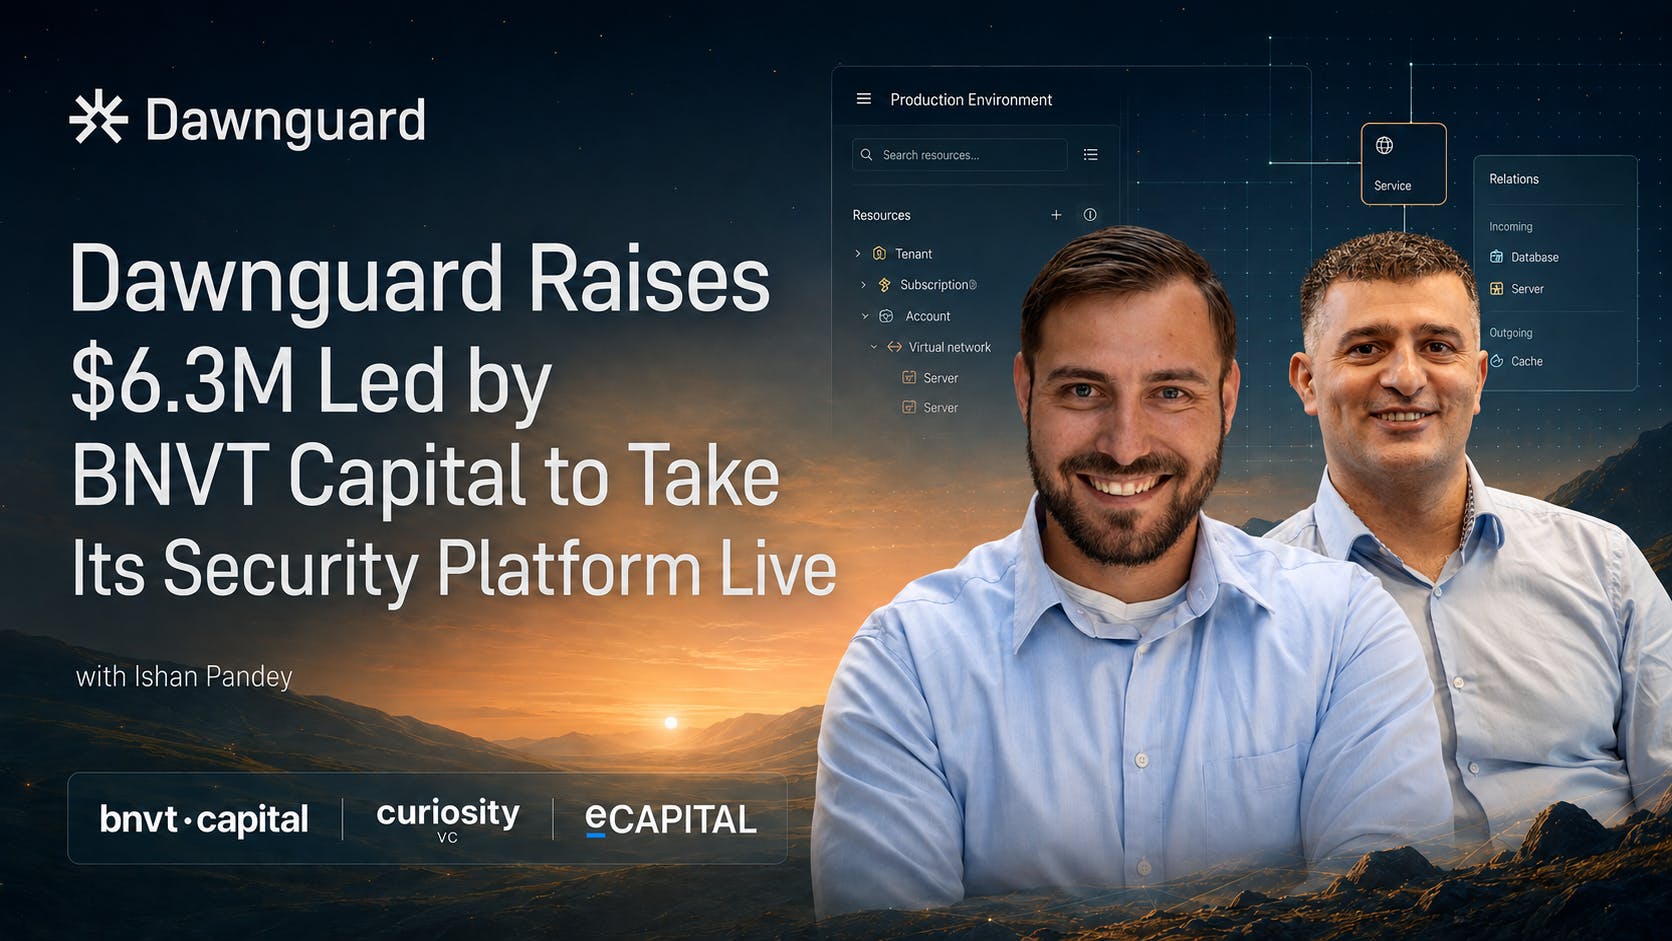
Today's cybersecurity news is split between structural vulnerabilities in LLMs and the real-world consequences of AI-generated code. A new paper shows BPE tokenization creates exploitable gaps in safety alignment, while another researcher found a guardrail bypass in ChatGPT's file download flow. Meanwhile, Dawnguard's funding round highlights the 13x surge in AI-code vulnerabilities, and the US government confirms another breach.

In today's edition: LLM vulnerabilities, AI-code risks and funding and Government breaches and training, plus quick bites.

Undercodetesting, Hackernoon, Techcrunch and 2 more

LLM vulnerabilities

Two pieces today expose fundamental weaknesses in how LLMs handle safety boundaries.

AI-code risks and funding

The surge in AI-generated code vulnerabilities is drawing venture capital and scrutiny.

Government breaches and training

Nation-state threats and capacity-building efforts round out the day.

techcrunch.com · 3 min

0
US government says it got hacked — again

The Department of Homeland Security is investigating a cyberattack on its Homeland Security Information Network (HSIN), a platform for federal, state, and local intelligence sharing. A senior lawmaker warns the breach could risk national security.

Quick bites

Tuesday

30 Jun's edition

Security · 7 stories