CVE-2026-97229: Critical Unauthenticated Remote Code Execution in GitLab›via Rapid7

 NetmanageITGitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
today· By Daniel Bender
0
NetmanageITGitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server CodeThe findings highlight how AI-generated and vibe-coded apps can spill and expose users' data when not configured or secured properly.
 Shared by @bugxhunter.bsky.social ↗
 theregister.com1mo ago
 Shared by @reconbee.bsky.social ↗
 reconbee.com1mo ago
 Shared by @ransomwaresommelier.com ↗
 group-ib.com1mo ago
 github.com1mo ago
 PYMNTSBanking Regulators Tighten Oversight of Possible AI Risks
 KFGOExclusive-Banking watchdogs ramp up AI scrutiny as stability fears mount, sources say
BdThemes supply chain attack poisoned JSON API exploiting XSS vulnerability to create rogue WordPress admin accounts and install webshells.
 techjuice.pk·@sipirtu.com·1mo ago·3 min read
PsiQuantum’s $1 billion funding round and 2027 target date for a quantum computer mean cryptographically relevant quantum computing (CRQC) is much closer than expected. With the quantum threat accelerating, organizations must make PQC migration a top prio
 iq.fp2.dev·@informaq.bsky.social·1mo ago·3 min read
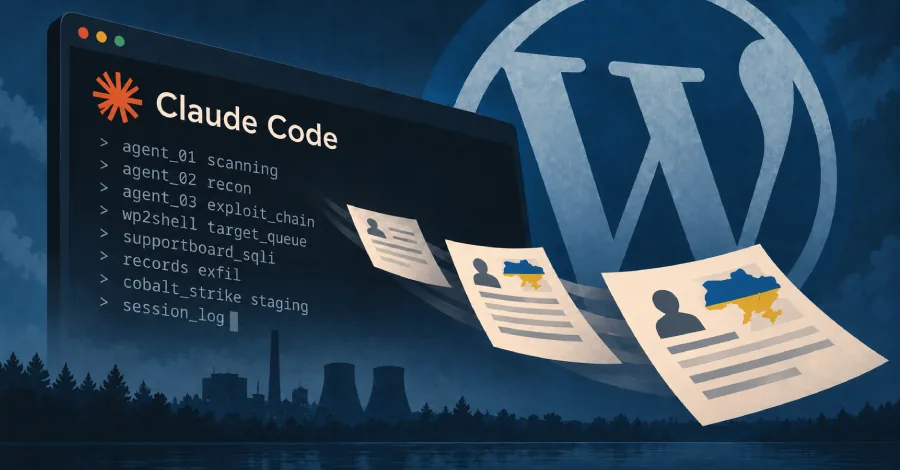
 thehackernews.comCyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records
 it-connect.techCyberXero Used 51 Claude Code Agents to Attack WordPress and Ukraine
 eSecurity PlanetCyberXero Uses Claude Code in Theft of 628,000+ Ukrainian Records
 Shared by @alexisrjimenez.bsky.social ↗
 thenextweb.com1mo ago
 Shared by @hipaajournal.bsky.social ↗
 zurl.co1mo ago
 Shared by @petersuciu.bsky.social ↗
 news.clearancejobs.com1mo ago
 Shared by @dustcircle.bsky.social ↗
 calcalistech.com1mo ago
 Shared by @helpnetsecurity.com ↗
 Help Net Security1mo ago
 Shared by @cysecuritynews.bsky.social ↗
 cysecurity.news1mo ago
 the420.inHackers Exploit Critical Bricksforge WordPress Flaw Allowing Remote Code Execution
 Arabian PostAttackers exploit Bricksforge flaw to breach WordPress websites
 scworld.comCritical Bricksforge WordPress flaw exploited in attacks
 Shared by @r-blueteamsec.bsky.social ↗
 huntress.com1mo ago
Autonomous penetration-testing agents rely on target responses. These responses guide both subsequent actions and the final report. A deceptive response can therefore redirect both the attack trajectory and the agent's verification process. However, final
 Shared by @ai-firehose.column.social ↗
 arxiv.org1mo ago
 Rapid7
 news4hackers.com
 Security.io
 deutschlandinenglish.com
 TechRadar

 Cyprus Mail
 globalbankingandfinance.com
 Protect.Computer