Banking Regulators Step Up AI Scrutiny Over Cyber and Stability Risks›via the420.in
More on this topic5 sources · 5 articles
The findings highlight how AI-generated and vibe-coded apps can spill and expose users' data when not configured or secured properly.
Meta says it issued a fix for the Muse zero-day vulnerability that would have let attackers do “whatever” they wanted on a victim’s Mac, highlighting the inherent dangers of AI helpers.
 Shared by @dailycamera.com ↗
 dailycamera.com1mo ago
 Shared by @ivezic.bsky.social ↗
 postquantum.com2mo ago
 NetmanageITGitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
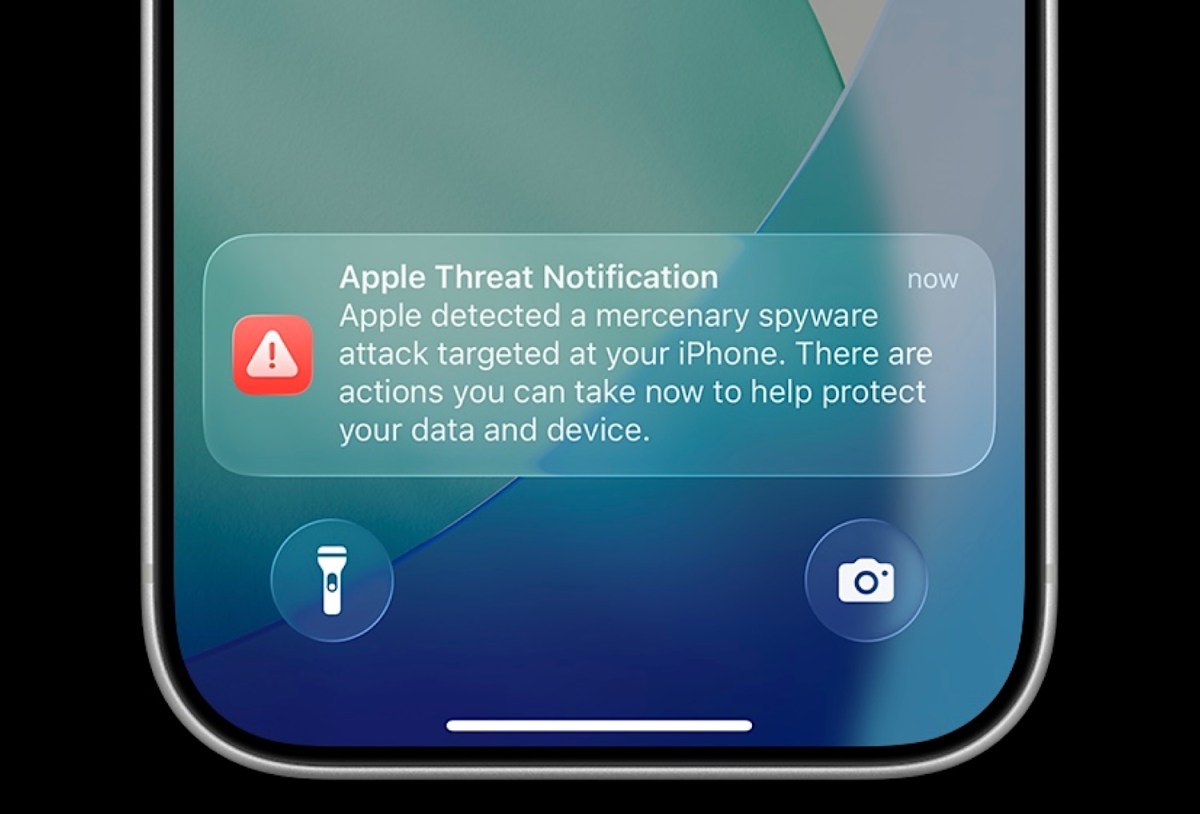
Apple now sends out push notifications to iPhone lock screens when the company identifies government spyware targeting someone's devices.
 @techcrunch.com·2mo ago·3 min read
A transparent, under-the-hood look at Echo's CVE reduction loop: multi-scanner detection, safe version bumps, custom backporting, and continuous automated syncing for NanoClaw.
 echo.ai·Hacker News: Front Page·2mo ago·11 min read
 Shared by @cryptocoverage.bsky.social ↗
 cryptocoverage.com2mo ago
 Shared by @thenewoil.org ↗
 cyberinsider.com2mo ago
 Shared by @utilityaccount27b6.bsky.social ↗
 Lifehacker2mo ago
Today, we moved to a new GPG signing subkey used to sign certain Firefox and Thunderbird artifacts (namely Linux tarballs, RPM packages, checksums files) after an unencrypted copy of the ...
 blog.mozilla.org2mo ago
 bobdahacker.com2mo ago

 Shared by @digitalfoundry.bsky.social ↗
 digitalfoundry.net2mo ago
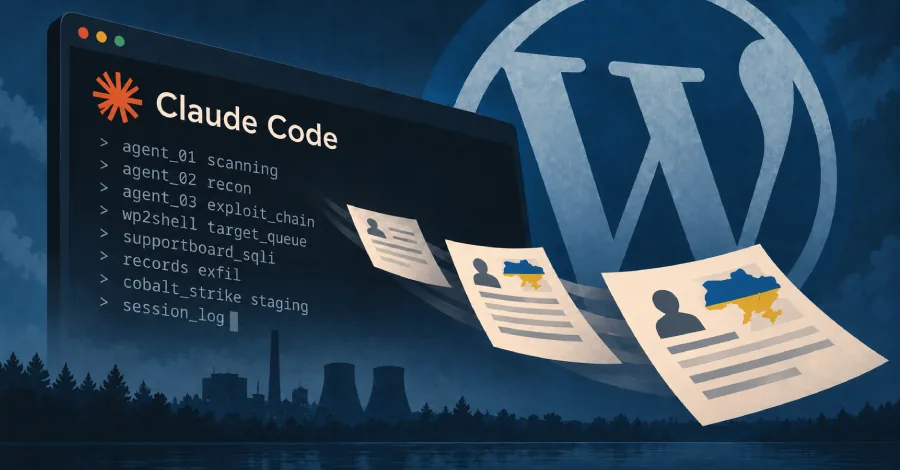
 thehackernews.comCyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records
 it-connect.techCyberXero Used 51 Claude Code Agents to Attack WordPress and Ukraine
 eSecurity PlanetCyberXero Uses Claude Code in Theft of 628,000+ Ukrainian Records
 Shared by @ninjaowl.ai ↗
 wired.com2mo ago
 Shared by @stackflag.bsky.social ↗
 stackflag.com2mo ago


 Cyprus Mail
 the420.in
 PYMNTS
 globalbankingandfinance.com

 news4hackers.com
 Asianet Newsable
 Rapid7
 Security.io
 deutschlandinenglish.com
 TechRadar

 Protect.Computer